
Hackers hijacked HBO Max's Reddit account to push ClickFix ads that deliver infostealer malware.
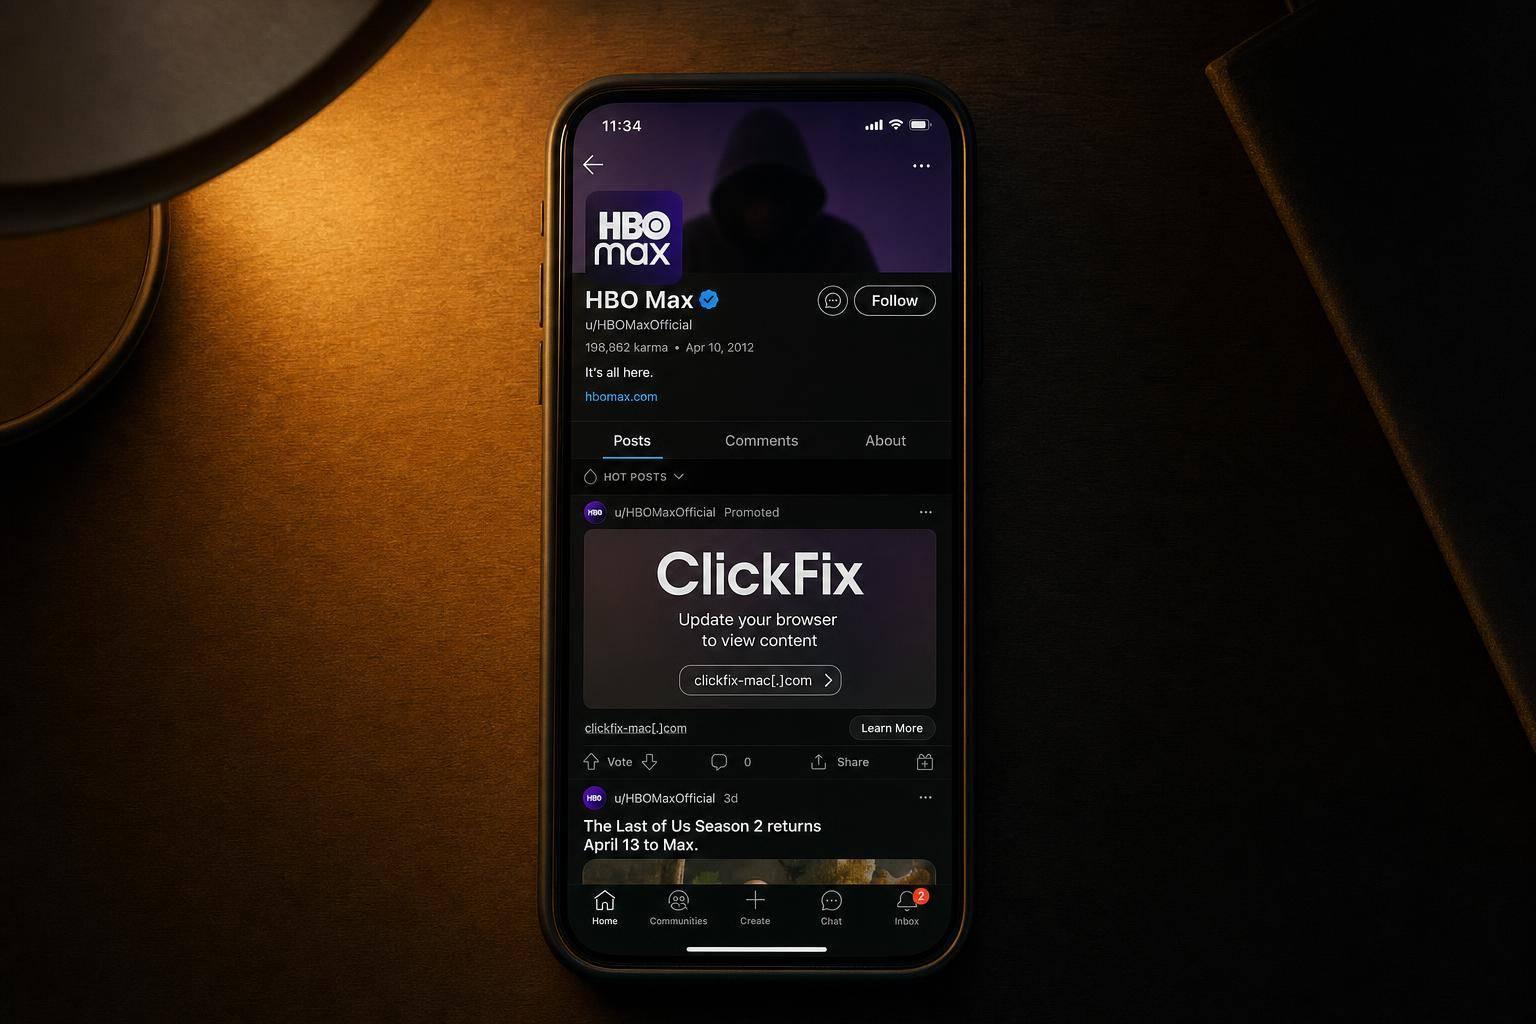
Attackers took over the verified official HBO Max Reddit account, u/hbomax, and used its advertising access to run a 48-hour malvertising campaign that pushed information-stealing malware to macOS and Windows users, according to researchers at Hudson Rock and ADAMnetworks.
The campaign came to light after a Reddit user reported suspicious ads on September 6. In a post cited by the researchers, the user wrote: "I was browsing Reddit and saw an ad displaying u/hbomax as the author – this advertised a macOS HBO Max app which I’d not heard of and was interested in. The user is verified and appears to have posted many times in the official HBO Max subreddits", wrote the user.
The user said the ad linked to hbomaxx[.]us, "which looks somewhat legitimate, and has a join button / download." According to the user, "clicking these opens up the classic infostealer/clickfix paste this command to download." They added: "Having checked, this downloads an executable with other capabilities for account compromise", done in a sandbox, "inspecting the output only, not running anything."
"My guess is that the reddit account is compromised", warned the user.
Researchers said the compromised account delivered 108 distinct ClickFix ads over a 48-hour period as part of a broader operation they named PasteSwitch.
"The threat actors squeezed as much value as possible out of the verified account’s status, pivoting quickly when domains were burned", Hudson Rock said.
Of those 108 ads, 46 used an HBO Max lure and were split between hbomaxx[.]app and hbomax-macos[.]com. Another 36 impersonated OpenAI Codex and directed users to codex-craft[.]com. The remainder included 15 ads for a fake macOS disk utility at apple.clean-disk-guide[.]com and 11 for other developer tools at code-desktop[.]com.
The HBO Max-themed ads were only one route into the larger PasteSwitch operation, which the researchers said had also appeared in fake Claude, Codex, Alfred, Homebrew, GitHub, utility, and wallet applications.
ADAMnetworks said it traced the copied command into "a cross-platform delivery operation spanning MacSync, AMOS, Amatera, fake wallet apps, and contract-controlled cryptocurrency clippers."
Researchers said the operation filtered visitors before showing malicious content. Depending on browser, screen, and device signals, some users were shown the lure and a malicious command, while others were shown a blank page, redirected to a legitimate vendor site, or served unrelated content.
The article said PasteSwitch used commands on macOS that piped curl output into zsh, allowing attacker code to run without a separate download step. Researchers identified three main payloads.
One, MacSync, used transaction tokens to track infected devices and exfiltrated stolen data in chunks. It gathered browser credentials, Gecko profiles, Telegram data, Apple Notes, and macOS passwords, storing the material in a hidden zip file before sending it out.
Another, AMOS Helper, installed itself as a persistent background process disguised as a macOS system service and then contacted attacker infrastructure for further tasks.
The campaign also used fake wallet apps posing as Ledger, Trezor Suite, and Exodus to collect 12- and 24-word BIP39 recovery phrases.
Windows users, meanwhile, were sent through a separate chain involving mshta and PowerShell that ended with a memory-running loader installing Amatera, malware that fingerprints the host, takes screenshots, and decrypts stored browser credentials.
The operation also included clipper malware, AnimateClipper and ZigClipper, which swaps a copied cryptocurrency wallet address with one controlled by the attacker. Instead of relying on a fixed command-and-control domain, the operators stored that address in smart contracts on the Binance Smart Chain.
"Between March and July 2026, researchers observed 36 mainnet changes executed by the same attacker controller address. Because the C2 domain is hosted directly on the blockchain, the infrastructure demonstrates dynamic resilience, allowing the threat actors to easily rotate burned domains", Hudson Rock added.
Reddit has since paused the ads and secured the account. "but the campaign proves once again why trusted distribution channels are becoming prime targets for infostealer delivery", Alon Gal, Hudson Rock CTO, wrote on LinkedIn.
Need pricing details?
EnrouteViewMedia is a Canadian technology company based in Edmonton, Alberta, Canada. The company was founded by a group of media entrepreneurs and engineering executives. Our mission is developing leading-edge digital media display technologies for taxicab rooftops and taxicab interiors advertising market. Through our easy to use ad delivery and management system, we assist our clients in reaching their customers with targeted exposure. EnRouteViewMedia continuously strives to be the global leader in digital geo-time targeted advertising media systems for modern taxi fleets.